15·
19 days ago

Yes, there are some to choose from. Though if you want to make games you probably want to use Godot instead. It’s language, gdscript, is like python
Lmao. Though other instances shouldn’t just accept timestamps from the future, either override it or reject it entirely
It looks like the image in the original comment is proxied by lemmy.zip rather than directly fetched from lemmy.world
It seems to depend on the instance too, like it works fine when viewed on feddit
Is this not an issue with the lemmy-ui? This issue describes a similar problem with links to posts from piefed users, which I made on lemmy iIrc, and the link in it still looks broken in the lemmy-ui.
Though I don’t have the context of the file you pointed out; Github is down lol
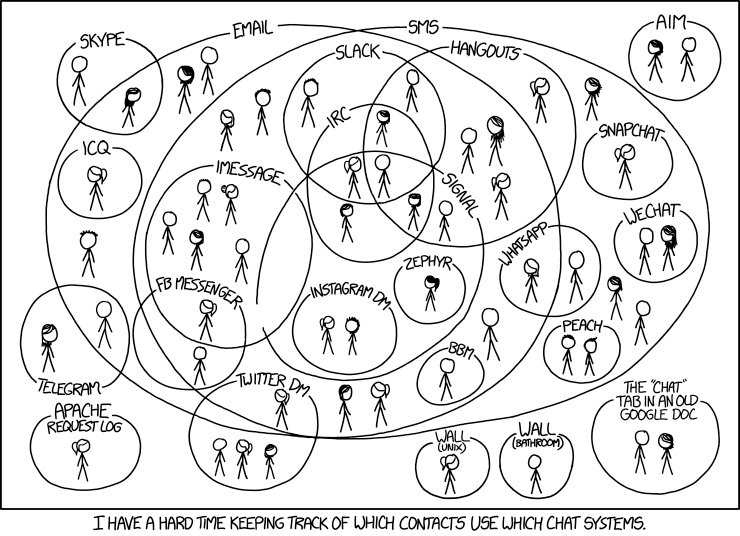
Yes, there is a page on there about xkcd as a whole, though the Wikipedia page is more expansive in that case: https://en.wikipedia.org/wiki/Xkcd
You can check out the explainxkcd link in the post. That site has explanations for all the xkcd comics
You can find it at !neinhole@horp.sciops.net
A very elaborate roundabout for sure
Factors may also be the higher fuel prices and being unable to fit inside a parking building

Using an RPi with a transistor almost seems professional… ITAPPMONROBOT
Fedora’s choice to have ptrace_scope 0 sure is strange, it seems they had a discussion about it to revert it back to the upstream default of 1.
SEL being important was actually the main reason why in the light of recent kernel vulnerabilities I switched back to openSUSE, after being on Void for a while as inspired by this guide.
That the AUR is insecure lays basically in its name, I really don’t get why people would use for anything but the most niche packages.
What Android is doing well compared to Linux is that it has proper per application compartmentalization, whereas *nix systems would require each program to be run by a different user to separate them, though Linux is also improving in that regard, for example through SEL or the flatpak sandbox.
If security is your first priority you really just gotta stop using a networked computer, and even an airgapped one would be risky
I mean it’s commendable that Apple makes an effort to keep their users secure from third-party attackers (besides MDM software), but there’s just no telling how much control and privacy violation is going on when they’re keeping their source code secret. (“What do they have to hide? Clearly something.”)
SecureBlue seems interesting, though most of their features look like security theater compared to the default
MacOS, iOS
Do you have a source for that beyond shills and their marketing?
There most definitively are vulnerabilities and backdoors in these OSes. Whether or not we hear of them doesn’t prove otherwise